Sectors
Every industry runs on different systems, answers to different regulators and faces different threats. We bring the same security-first engineering to each, shaped around what your sector actually demands.
- sectors we specialise in
- 5sectors we specialise in
- services, one accountable team
- 6services, one accountable team
- regulation and standards built in
- UKregulation and standards built in
Why sector matters
The same technology, very different stakes
A cloud platform, a Teams rollout or an AI assistant looks similar on paper whichever organisation it's for. In practice, the stakes are very different. In a hospital, downtime can delay treatment. In a bank, it can breach operational resilience rules. In retail, a few hours offline at peak can wipe out a season's margin. For a council or government body, it can stop citizens getting help when they need it most.
That's why we start every engagement with your sector's realities: the regulators you answer to, the data you hold, the threats that target organisations like yours, and the systems you can't afford to lose. Our cybersecurity, cloud, software and AI teams then design around them from the start, so compliance and resilience are built in rather than bolted on.
Regulation-aware
From NHS DSPT to FCA operational resilience and PCI DSS, we design to the rules your sector is measured by.
Security-first
We come from cybersecurity, so protecting sensitive data and critical services shapes every decision.
AI with guardrails
Practical AI that saves time and improves decisions, with the governance your auditors and customers expect.
Built to stay up
Resilient architecture, monitoring and tested recovery for the services people rely on.
Board-level ownership of cyber risk varies widely by sector
More than half of finance and insurance businesses have a board member responsible for cyber security. In retail and wholesale it's closer to one in five, despite the attacks the sector saw in 2025.
Source: DSIT, Cyber Security Breaches Survey 2025
| Sector | Share |
|---|---|
| Finance | 57% |
| Professional services | 36% |
| Health and care | 34% |
| All businesses | 27% |
| Retail | 22% |
The bigger picture
Threats are rising. So is what AI can do.
204
nationally significant cyber incidents handled by the NCSC in a year, up from 89: about four a week
Source: NCSC Annual Review 2025
35%
of UK businesses with 10 or more staff now use AI, up from around 12% in late 2023
Source: ONS, Artificial intelligence in UK businesses, 2023 to 2026
$1.9m
average saving per breach for organisations using security AI and automation extensively
Healthcare
Secure, available systems for care providers
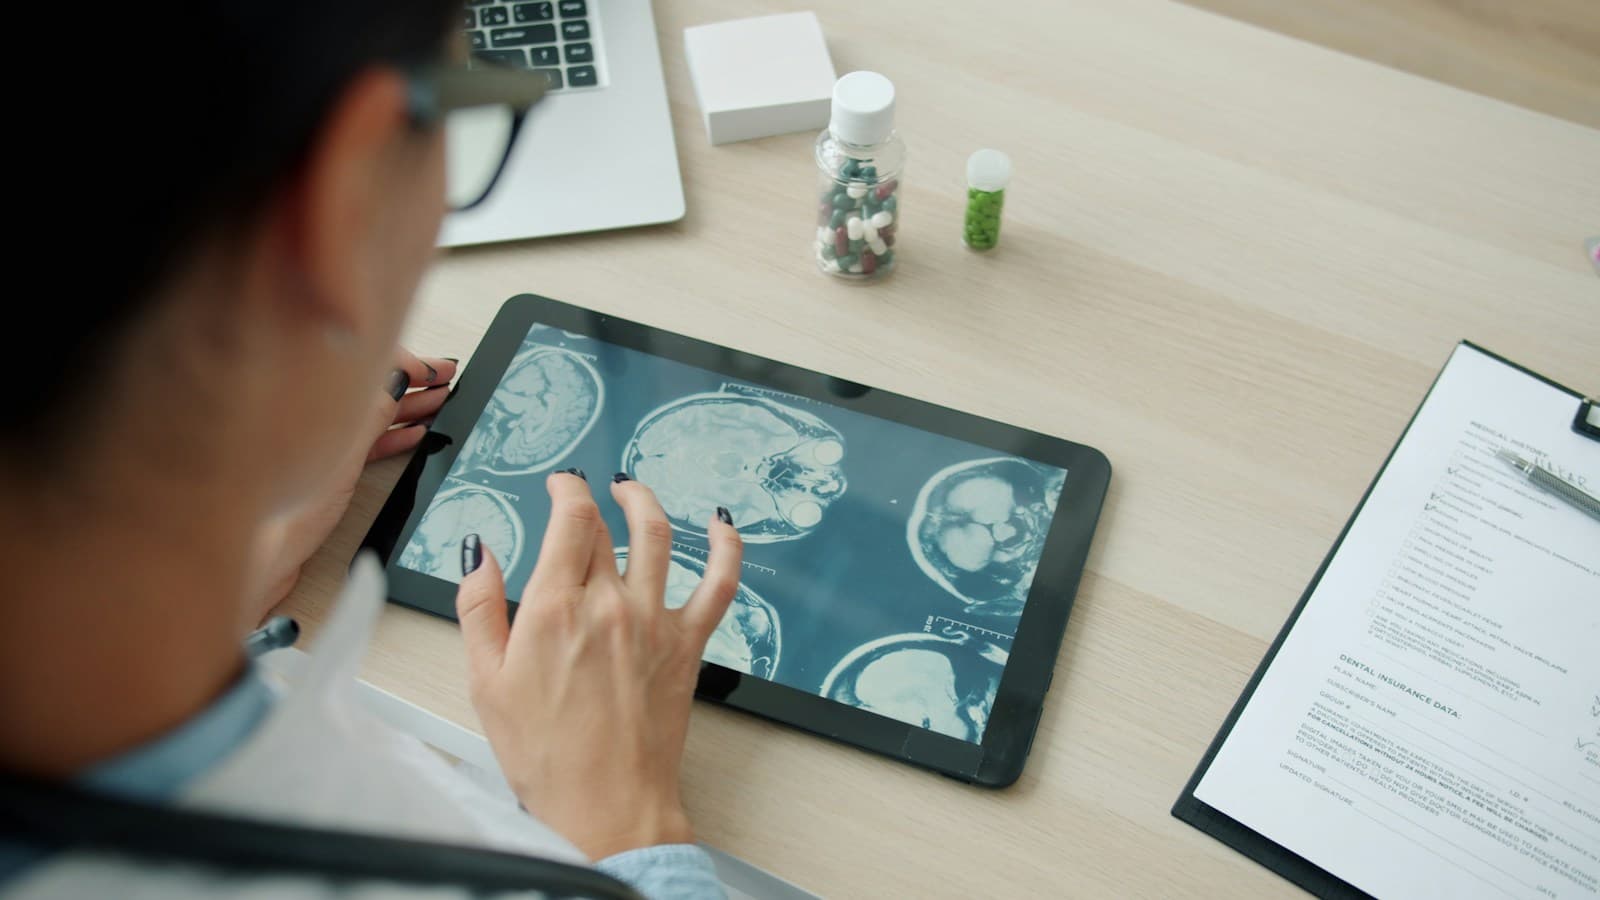
Healthcare runs on technology: electronic patient records, pathology and imaging systems, e-prescribing, video consultations and a growing web of connected devices. When these systems are unavailable, care is delayed. When they're breached, some of the most sensitive data there is gets exposed.
We help NHS organisations, private providers, care groups and health technology companies secure their systems, integrate them safely, and adopt AI in ways clinicians can trust, with the evidence regulators and commissioners ask for.
The challenges
- Ransomware aimed at hospitals and their suppliers
- Legacy clinical systems that are hard to patch
- Special category patient data under UK GDPR
- Integrating records, devices and third-party apps
How Anthrasec helps
- Managed CybersecurityRound-the-clock monitoring, response and supplier risk management
- Enterprise InfrastructureResilient networks, tested backups and recovery for clinical systems
- Application DevelopmentSecure patient portals and interoperable integrations
- AI & AutomationAdmin automation and AI tools with clinical safety in mind
Where AI helps in healthcare
- Automating referrals, letters and back-office admin
- Supporting imaging and triage alongside clinicians
- Forecasting demand, beds and staffing
$7.42m
average cost of a healthcare data breach, the highest of any industry for the 15th year running
10,152
outpatient appointments postponed at two London trusts after the 2024 Synnovis ransomware attack, plus 1,710 elective procedures
3×
more stroke patients recovering with no or slight disability (16% to 48%) with AI imaging support, and treatment over an hour faster
Source: GOV.UK, Artificial intelligence revolutionising NHS stroke care
Frameworks we help you align with
- NHS Data Security and Protection Toolkit
- DCB0129 and DCB0160 clinical safety
- NHS DTAC
- UK GDPR
- Cyber Essentials Plus
- NIS Regulations
Retail
Commerce that holds up at peak
Modern retail is a single system that customers experience through many doors: websites, apps, stores, marketplaces, payments, warehouses and loyalty schemes. Every one of those doors is also a way in for attackers, and every minute of downtime at peak is revenue that doesn't come back.
We help retailers and consumer brands scale their platforms, protect payments and customer data, strengthen the help desks and identities attackers target, and use AI to forecast demand and serve customers better.
The challenges
- Traffic spikes at peak trading and launches
- Social engineering of help desks and suppliers
- Card and online payment fraud
- Connecting stores, e-commerce and fulfilment
How Anthrasec helps
- Cloud PlatformsPlatforms that scale for peak, with costs that scale back down
- Managed CybersecurityIdentity protection, help-desk hardening and 24/7 detection
- Application DevelopmentFast, accessible e-commerce and customer apps
- AI & AutomationDemand forecasting, personalisation and customer service
Where AI helps in retail
- Forecasting demand and stock by store and channel
- Personalised recommendations and search
- AI assistants for customer service
£300m
M&S's initial estimate of the hit to operating profit from its April 2025 cyber attack
6.5m
Co-op members whose personal data was stolen in a 2025 cyber attack
Source: TechCrunch, Co-op confirms member data stolen, July 2025
22%
rise in remote purchase fraud cases in 2024 as criminals targeted online payments
Frameworks we help you align with
- PCI DSS v4.0
- UK GDPR and PECR
- Cyber Essentials
- ISO/IEC 27001
- WCAG 2.2 AA
Finance
The resilience regulators expect
Financial services firms are among the most targeted and most regulated organisations in the UK. Regulators expect firms to stay within impact tolerances for their important business services, manage third-party and AI model risk, and prove it, while fraudsters test every channel for weaknesses.
We help banks, insurers, wealth managers, payment firms and fintechs build resilient, well-evidenced technology, detect threats and fraud faster, and adopt AI with the governance and explainability the FCA and PRA expect.
The challenges
- Operational resilience and impact tolerances
- Fraud and account takeover across channels
- Third-party, cloud and outsourcing risk
- Governing AI and model risk
How Anthrasec helps
- Managed CybersecurityThreat detection, testing and audit-ready evidence
- Cloud PlatformsResilient, well-governed cloud with clear exit plans
- Enterprise InfrastructureHardened infrastructure mapped to important business services
- AI & AutomationExplainable AI for fraud, operations and customer service
Where AI helps in finance
- Real-time fraud and anomaly detection
- Automating KYC, onboarding and document checks
- Assistants that help staff answer customers faster
75%
of UK financial services firms already use AI, and a further 10% plan to within three years
Source: Bank of England and FCA, AI in UK financial services 2024
£1.17bn
stolen through fraud in the UK in 2024, while banks prevented a further £1.45bn of unauthorised fraud
£5.74m
average cost of a data breach for UK financial services, the costliest UK industry
Frameworks we help you align with
- FCA and PRA operational resilience
- PRA SS2/21 outsourcing
- PRA SS1/23 model risk
- DORA
- Consumer Duty
- PCI DSS v4.0
Corporate
Modern IT for growing organisations
Professional services firms, technology companies and growing businesses depend on their people being productive wherever they work, and on keeping client data safe. Many have outgrown the IT that got them started: scattered tools, unmanaged devices and security that relies on everyone being careful.
We help organisations modernise their workplace and cloud, secure identities and devices, meet the security demands of larger clients, and put AI to work across everyday processes with sensible guardrails.
The challenges
- Clients demanding proof of security
- Hybrid working on unmanaged devices
- Staff using unapproved AI tools
- Legacy systems slowing growth
How Anthrasec helps
- Modern WorkplaceMicrosoft 365, Teams and managed, secure devices
- Managed CybersecurityCyber Essentials, ISO 27001 readiness and monitoring
- Cloud PlatformsMigration and cost-efficient cloud that scales with you
- AI & AutomationCopilot readiness and workflow automation
Where AI helps in corporate
- Copilots for drafting, summarising and research
- Automated proposals, reporting and finance admin
- Knowledge assistants over your own documents
75%
of knowledge workers already use generative AI at work
43%
of UK businesses identified a cyber breach or attack in the last 12 months
Frameworks we help you align with
- Cyber Essentials
- ISO/IEC 27001
- SOC 2
- UK GDPR
- ISO/IEC 42001 (AI management)
- NCSC Cyber Governance Code of Practice
Public sector
Dependable services for citizens
Central government, local authorities, arm's-length bodies and education providers deliver services people can't simply go elsewhere for. Many still depend on ageing systems, face a severe and growing cyber threat, and must do more with constrained budgets and scarce specialist skills.
We help public bodies modernise legacy systems in manageable stages, strengthen cyber resilience against recognised government frameworks, build accessible digital services, and explore AI transparently and responsibly.
The challenges
- Legacy systems with unfunded remediation
- A severe and advancing cyber threat
- Scarce specialist skills
- Accessibility and transparency duties
How Anthrasec helps
- Managed CybersecurityCyber resilience aligned to the Cyber Assessment Framework
- Application DevelopmentAccessible digital services built to the GOV.UK Service Standard
- Enterprise InfrastructureStaged legacy modernisation with no big-bang risk
- AI & AutomationTransparent, well-governed AI for casework and admin
Where AI helps in public sector
- Triaging and routing citizen enquiries
- Summarising casework and correspondence
- Finding and extracting data from documents
58
critical government IT systems assessed in 2024 had significant gaps in cyber resilience
Source: National Audit Office, Government cyber resilience, January 2025
228
legacy IT systems in government departments, with no fully funded remediation plans for half of them
Source: National Audit Office, Government cyber resilience, January 2025
37%
of government bodies had deployed AI, and 70% were piloting or planning it
Source: National Audit Office, Use of AI in government, March 2024
Frameworks we help you align with
- Cyber Assessment Framework and GovAssure
- GOV.UK Service Standard
- Technology Code of Practice
- WCAG 2.2 AA and accessibility regulations
- Algorithmic Transparency Recording Standard
- Cyber Essentials
AI in practice
When AI is done well, the results are measurable
AI imaging software now supports stroke specialists across every stroke network in England. Where it's used, patients reach treatment more than an hour sooner, and three times as many recover with no or only slight disability. It's a model for sector AI done properly: clinicians stay in control, the technology is assessed for safety, and the outcome is measured.
- Start with a measurable outcome, not the technology
- Keep experts in the loop for decisions that matter
- Build in safety, privacy and security from day one
Source: GOV.UK, Artificial intelligence revolutionising NHS stroke care
| Care pathway | Share |
|---|---|
| Before AI imaging | 16% |
| With AI imaging | 48% |
How we work
An approach built for regulated, high-stakes environments
- 01
Understand your sector
Your regulators, data, threats and critical services, mapped before any solution is proposed.
- 02
Assess and prioritise
A clear view of risk and compliance gaps, ranked by impact on your organisation.
- 03
Design and deliver
Secure, resilient solutions delivered in stages, with the evidence your auditors need.
- 04
Run and improve
Monitoring, support and regular reviews as regulations, threats and your goals change.
Why Anthrasec
A partner that speaks your sector's language
Security at the core
Cybersecurity is where we started, and it shapes every system we build and run.
Regulation built in
We design to the frameworks your sector answers to, not around them.
One accountable team
Security, cloud, infrastructure, software and AI together, with no gaps between suppliers.
Plain-English evidence
Clear documentation and reporting for boards, auditors and regulators.
Common questions
Working with Anthrasec in your sector
Which sectors does Anthrasec work with?
We work with healthcare providers and health technology companies, retailers and consumer brands, financial services firms, corporate and professional services organisations, and public sector bodies across the UK.
Do you work with regulated organisations?
Yes. Much of our work is for organisations with strict regulatory requirements. We design to frameworks such as the NHS Data Security and Protection Toolkit, FCA and PRA operational resilience rules, PCI DSS and the Cyber Assessment Framework, and provide the evidence you need to demonstrate compliance.
Can you help us adopt AI safely in a regulated sector?
Yes. We start with a measurable business outcome, assess data protection and security risks, keep people in control of important decisions, and document how the AI works, so you can explain it to regulators, auditors and customers.
We're a smaller organisation. Is sector expertise still relevant?
Very much so. Smaller organisations face the same regulations and many of the same threats as large ones, with fewer people to manage them. We scale our services to your size and priorities.
Are you certified under these frameworks?
We help clients prepare for and align with frameworks such as Cyber Essentials, ISO 27001 and PCI DSS. Certification itself is awarded to your organisation by independent, accredited bodies.
Work with us
Ready to work with Anthrasec?
Let's schedule a meeting.
Pick a time that suits you and tell us a little about what you need. We'll come prepared, with the right people in the room.
Step 1 of 4
Choose a date and time
October 2026
Checking availability…
Times are shown in UK time (London). Meetings are held on Microsoft Teams.
Available times
Choose a date to see available times.